

Awakening Security
Preface: Creative Security, New Horizons
From Information Security to AI Governance
Creative Security: New Horizons
In an age defined by digital transformation, information security is no longer just a technical necessity; it has become a strategic imperative. This is truer still for organisations that live on ideas: creative agencies, software teams and everyone building with AI today. Intellectual property, client data and innovative ideas are the real currency of success, and protecting them is part of making them.
This book grew out of three guides I wrote for security leaders: Creative Security, on applying ISO 27001:2022 in the creative industries; AppSec Mastery, on integrating an information security management system into software development; and AISEC Mastery, on applying ISO 42001:2023 to AI governance. Three doors to one house, so I brought them together here as one connected journey.
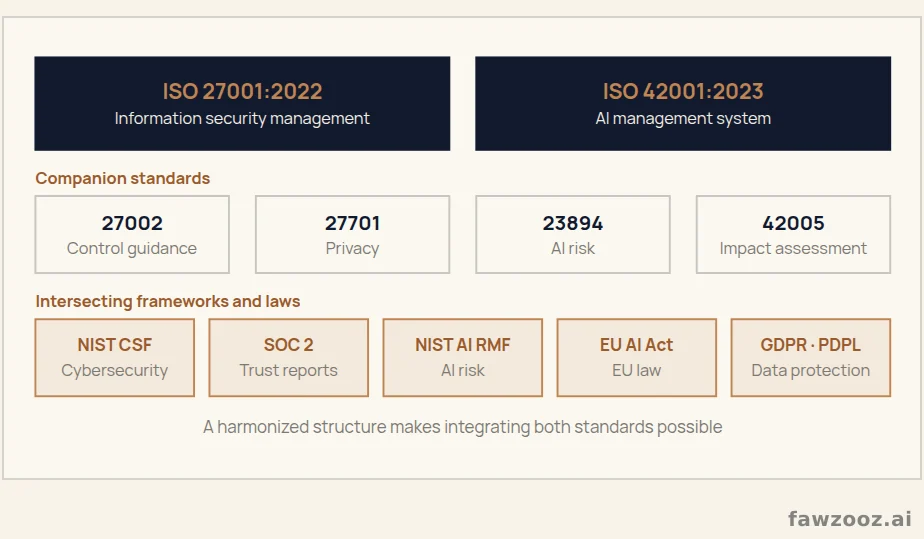
Text in this figure
ISO 27001:2022 · Information security management · ISO 42001:2023 · AI management system · Companion standards · 27002 · Control guidance · 27701 · Privacy · 23894 · AI risk · 42005 · Impact assessment · Intersecting frameworks and laws · NIST CSF · Cybersecurity · SOC 2 · Trust reports · NIST AI RMF · AI risk · EU AI Act · EU law · GDPR · PDPL · Data protection · A harmonized structure makes integrating both standards possible · Figure 1
Why “Awakening Security”?
Security that does not know what it protects, or why, turns into burdensome restrictions that people work around. Awakening security starts by understanding the asset: the idea, the code, the model and the data. Then it chooses the control that protects it without stifling creativity. It is a natural extension of Awakening Intelligence: there we learned to use intelligence consciously; here we learn to protect what we build with it.
Why a Second Edition?
Since Creative Security appeared in 2025, generative AI has entered every studio and development office, and prompts, models and agents have become assets that need protection and governance. This edition therefore brings together every concept from the three books, updated, and adds a full part on ISO 42001, the first international standard for an AI management system, uniting both standards in one integrated system. I have also redrawn every concept as figures in a single visual language.
Awakening security does not slow creativity down; it gives it the confidence to dare.
How to Read This Book
The book has six parts that follow the management-system cycle itself: awareness of the landscape, building the foundation, planning risks and controls, operating in the field, governing AI, and sustaining it all through culture, measurement and improvement. Leaders can start with Parts One, Two and Six; developers and creatives with Parts Four and Five; freelancers can jump straight to Chapters 14 and 24.
- 2026 Update: A box adding what has changed in the standards and threats since the first editions.
- From the Field: A box warning of implementation pitfalls the standards do not mention.
- Lessons Learned: A summary at the end of every chapter.
- Appendices: Ready-made templates for risks, impact assessment and incidents, a standards mapping, and a glossary in English with its Arabic equivalents.
Tip: use ← → to move between sections.